 CYBERSECURITY · RISK · ASSURANCE
01 / LEADERSHIP↗
Virtual CISO & Security Governance
Senior security leadership, governance design, strategy, risk oversight and executive reporting.
Security roadmapsBoard-level oversight
Discuss security leadership ↗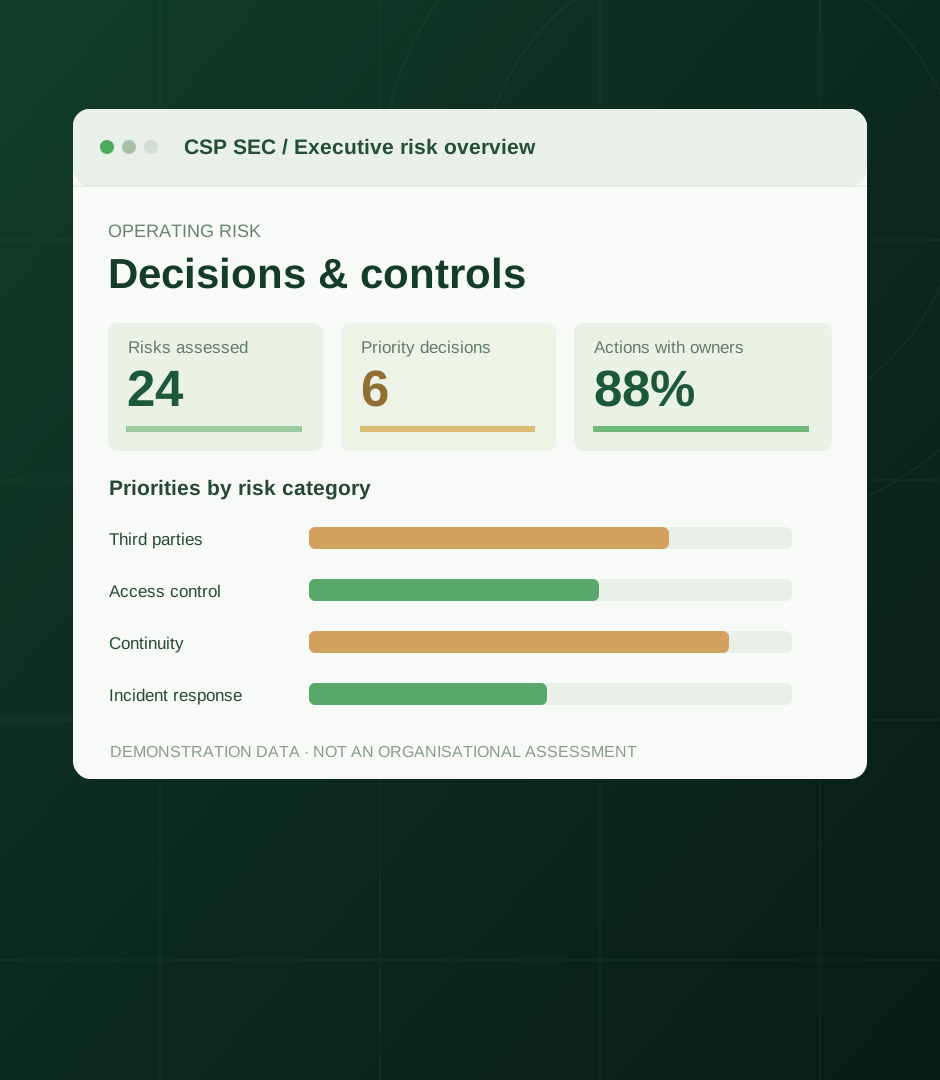 GOVERNANCE · AUDIT · COMPLIANCE
CSP SEC supports organisations with governance, management-system implementation, independent assessments and tailored training. We turn applicable requirements into accountable decisions, operating controls and evidence.
 STRATEGIC ADVISORYLeadership grounded in business priorities.Explore our services ↗
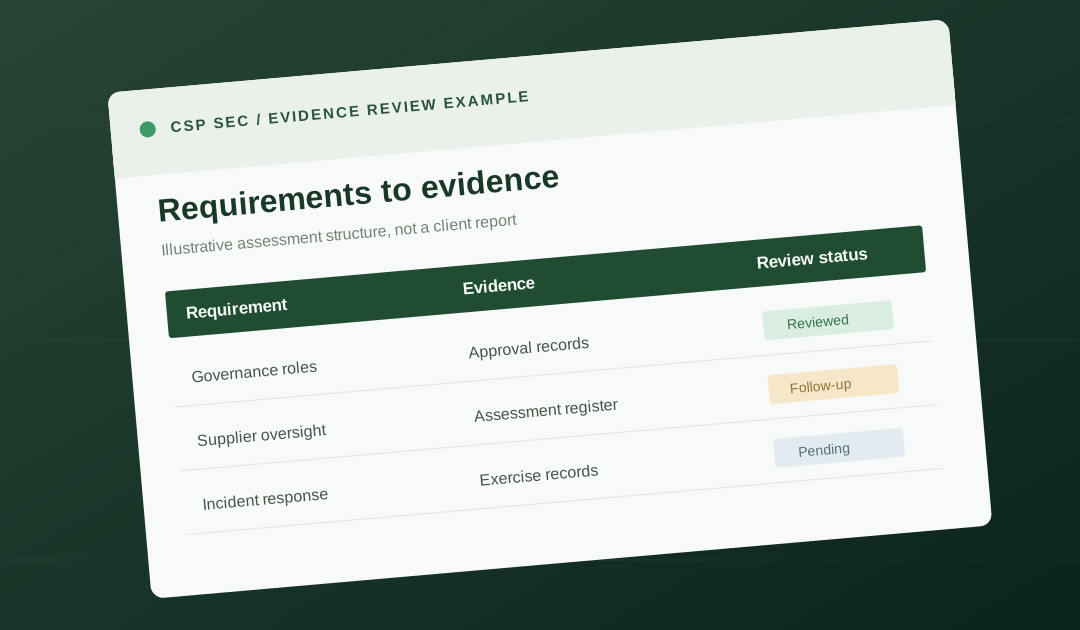 EVIDENCE & ASSURANCEFindings converted into owned actions.Explore dashboard examples ↗
 RISK & RESILIENCEPrepare for disruption. Protect what matters.Explore risk & continuity ↗
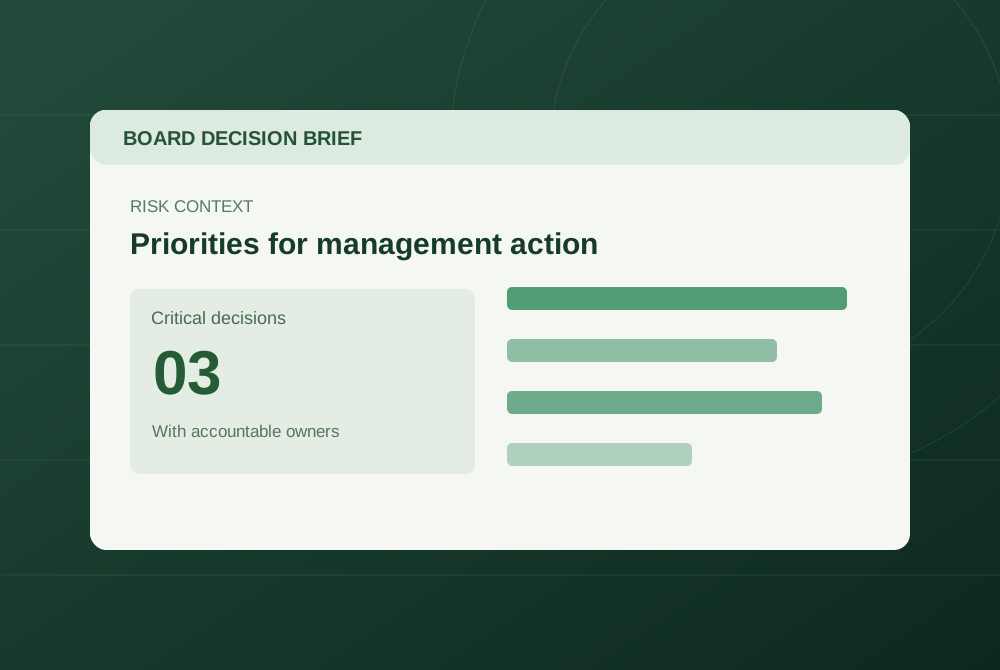
Illustrative imagery and sample materials. No client information is displayed.
START WITH THE BUSINESS CHALLENGE
Security and compliance work should start with a decision, risk or obligation, not a stack of documents. Choose the situation that best reflects your needs.
Establish governance, implement controls and prepare for certification or an external review.
Explore implementation ↗ 02 / DEMONSTRATEClarify obligations, identify gaps and establish reliable evidence for auditors or stakeholders.
Explore assessments ↗ 03 / LEADAccess fractional CISO, risk oversight and strategic guidance without building a full-time function.
Explore advisory ↗WHAT WE DO
Specialist services that bridge executive decisions, operational requirements and credible assurance. Tailored to your scope, risk and stage of maturity.
Senior security leadership, governance design, strategy, risk oversight and executive reporting.
Risk-based audits and evidence reviews to evaluate conformity, control effectiveness and gaps.
Design, implementation and improvement of information security, business continuity and quality management systems, including integrated systems and certification readiness.
GDPR, DORA, NIS2 and applicable Central Bank of Kosovo requirements, including practical gap assessments and implementation support.
Identify, evaluate and treat strategic, operational and information security risks using an organisation-wide approach.
Protect critical operations through business impact analysis, recovery strategies, continuity planning, crisis management and practical exercises.
Cloud and SaaS governance, supplier assurance, cloud privacy controls and SOC 2 readiness advisory.
Framework expertise without one-size-fits-all answers. Our work draws on relevant ISO standards, European regulation and recognised risk and assurance practices. We select what fits the organisation rather than forcing every client into the same checklist.
Explore our framework areas ↗RISK MANAGEMENT & BUSINESS CONTINUITY
Enterprise risk management supports informed decisions about uncertainty. Business continuity focuses on protecting and recovering critical operations when disruption occurs, beyond management system documentation.
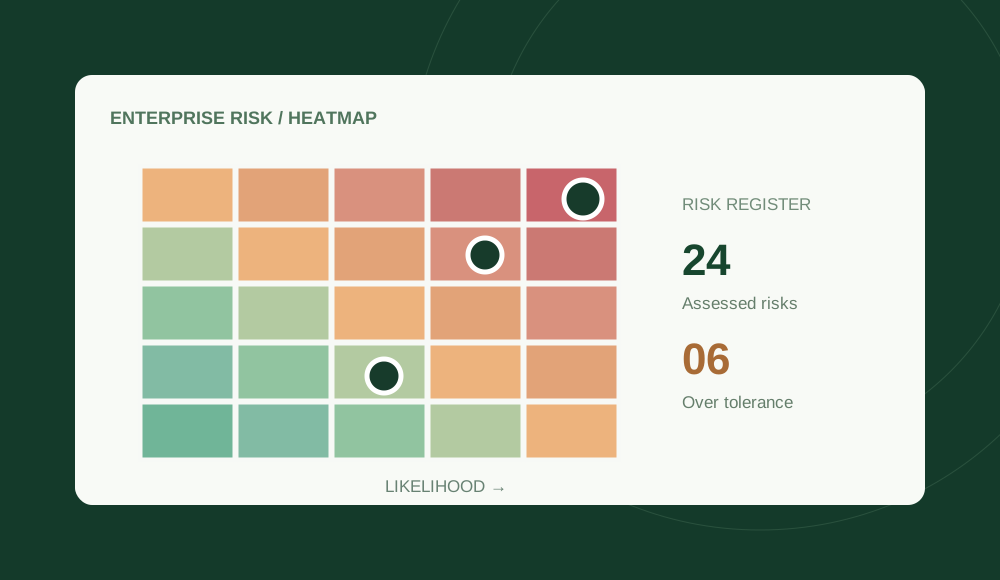 RISK ASSESSMENT / DEMO
01 / RISK MANAGEMENT
Establish risk criteria, maintain meaningful risk registers, select treatments and support management risk oversight.
Discuss risk management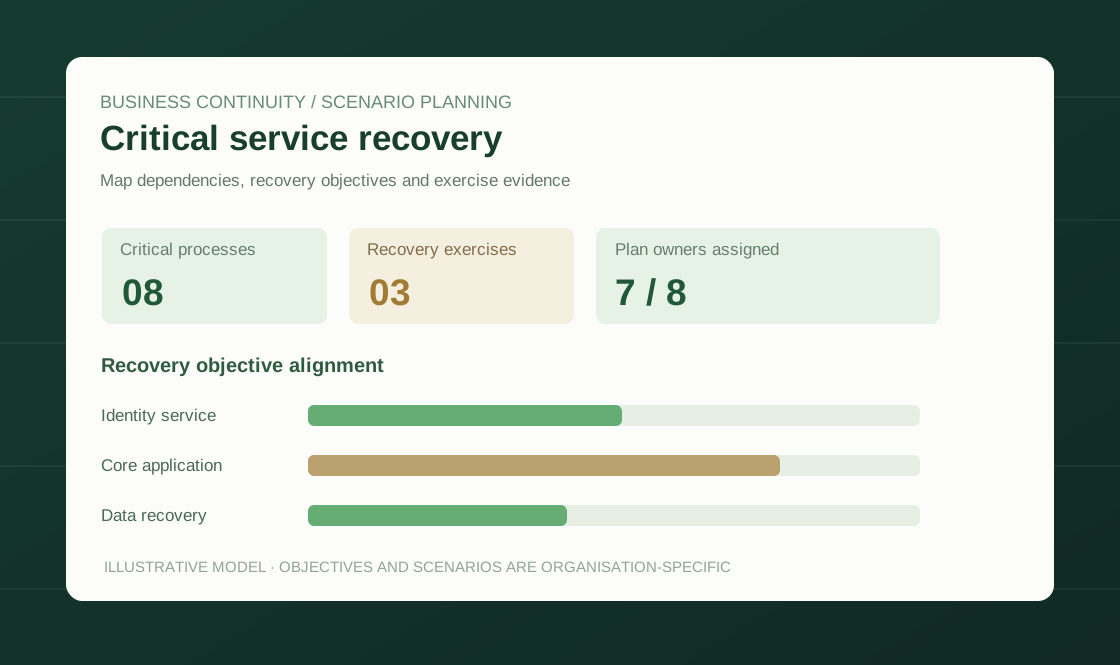 CONTINUITY PLANNING / DEMO
02 / BUSINESS CONTINUITY
Define recovery priorities through business impact analysis, develop continuity responses, exercise plans and review resilience evidence.
Discuss continuity & resilienceWHAT CLIENTS RECEIVE
Our deliverables connect requirements to responsible owners, operational decisions and evidence. The exact outputs depend on engagement scope and independence requirements.
A clear trail from the requirement and observed gap to risk, accountable owner, evidence and review.
Clear applicability decisions and actionable requirements, including relevant dependencies.
Risk ownership, rationale, priorities and documented treatment decisions.
Traceable control objectives, operating evidence and assigned responsibilities.
Documented findings, practical remediation and follow-up verification.
Concise reporting on risk exposure, compliance gaps and required decisions.
WHAT DECISION-MAKERS NEED TO SEE
See the types of evidence-led dashboards we can develop to help teams prioritise action, report progress and focus management attention.
CSP SEC / COMPLIANCE ASSESSMENT HUB
Use a free, browser-based readiness check to surface potential gaps. Then, where needed, move to a professional evidence-based assessment.
Explore key practices for lawful processing, governance, individual rights and security.
Assess selected financial-entity obligations or ICT supplier-assurance themes.
Review selected cybersecurity measures, subject to national-law applicability.
KOSOVO / FINANCIAL SECTOR
Preparing for Central Bank of Kosovo supervisory requirements? We support financial institutions with regulatory scope analysis, ICT risk governance, business continuity, evidence reviews and practical remediation planning.
Explore CBK assessment services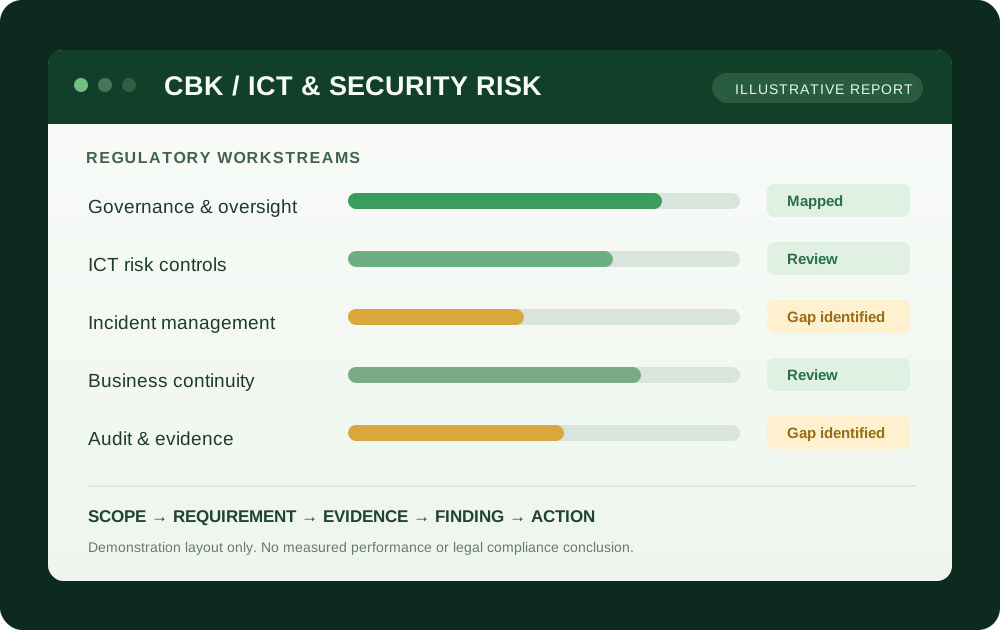 ILLUSTRATIVE REPORTING EXAMPLE
Preliminary result, not a compliance rating. Self-reported weighted readiness cannot establish GDPR, DORA or NIS2 compliance, audit findings or certification. Applicability and evidence need professional review.
Commission a scoped GDPR audit, DORA or NIS2 gap review, or CBK ICT and security risk assessment with evidence-based findings.
 ILLUSTRATIVE TRAINING VISUAL
CSP SEC / LEARNING & DEVELOPMENT
From PECB certification training to role-based in-house workshops, we help professionals and management teams build the understanding needed to put security, risk and regulatory requirements into practice.
STANDARDS & REGULATORY EXPERTISE
Rather than promote a fixed list of individual certificates on every page, we organise expertise around the business needs it supports. Below are representative areas, not an exhaustive catalogue or a claim of accredited certification.
Ask about a specific requirement ↗ISO/IEC 27001, ISO/IEC 27017 and ISO/IEC 27018; security and privacy governance for cloud and SaaS environments.
ISO/IEC 27001 (information security), ISO 22301 (business continuity) and ISO 9001 (quality); implementation and improvement of individual or integrated management systems.
ISO 31000-aligned risk management, business impact analysis, recovery strategies, resilience exercises and crisis management. ISO 31000 provides guidance, not management system certification.
GDPR, DORA, NIS2 and relevant Central Bank of Kosovo regulations; applicability analysis, control mapping and evidence-based assessment. SOC 2 readiness support is also available.
OUR WORKING METHOD
Our methodology is proportionate to each engagement. Implementation and independent audit services are scoped separately where necessary to preserve objectivity.
Business objectives, obligations, governance and risk context.
Processes, controls, dependencies and supporting evidence.
Proportionate measures, ownership, priorities and implementation.
Assess results, document findings and support improvement.
CSP SEC / INSIGHTS & ANALYSIS
Regulatory developments, implementation lessons and audit perspectives explained for decision-makers, not just specialists.
WHY CSP SEC
Experienced governance, risk, compliance and assurance support for organisations facing complex requirements.
Clients need more than a template or a high-level statement of conformity. They need experienced judgment about which requirements apply, which risks matter and what credible implementation looks like.
CSP SEC is led by a professional with more than 15 years of experience spanning security governance, regulatory supervision, organisational leadership and audit. We bring that perspective directly into our engagements.
PECB Chief Information Security Officer; ISO/IEC 27001 Lead Auditor; ISO 22301 Lead Auditor; ISO 9001 Lead Auditor; PECB Lead Cloud Security Manager; PECB ISO 31000 Lead Risk Manager. Qualifications belong to the individual professional, not to CSP SEC as an accredited certification body.
ENGAGEMENT OPTIONS
From targeted assessments to long-term advisory relationships, we agree scope, responsibilities, outputs and decision points before work begins.
A defined scope: gap analysis, implementation project, risk review or regulatory workstream.
Fractional CISO and continuing governance, risk and compliance support.
Appropriately scoped audits or objective reviews, with written findings and recommendations.
LET'S START WITH YOUR CHALLENGE
Whether you need a compliance assessment, stronger governance or senior security advisory support, tell us what you are working toward.
SEND A BUSINESS ENQUIRY
Prefer email? mentor.hoxhaj@csp-sec.com